Security & Performance
Revolte helps engineering teams detect, remediate, and validate security and performance issues across live systems - so every fix ships with proof attached.
Start Building
Built for teams who have to prove a system is safe and fast, not just report that it is

PERSONA
Security findings don't slow teams down. Unproven fixes do.
Every team already has scanners, dashboards, and a backlog of findings. What's missing is the path between them - a governed route from a real finding to a validated fix somebody is willing to sign off on.

HOW IT WORKS
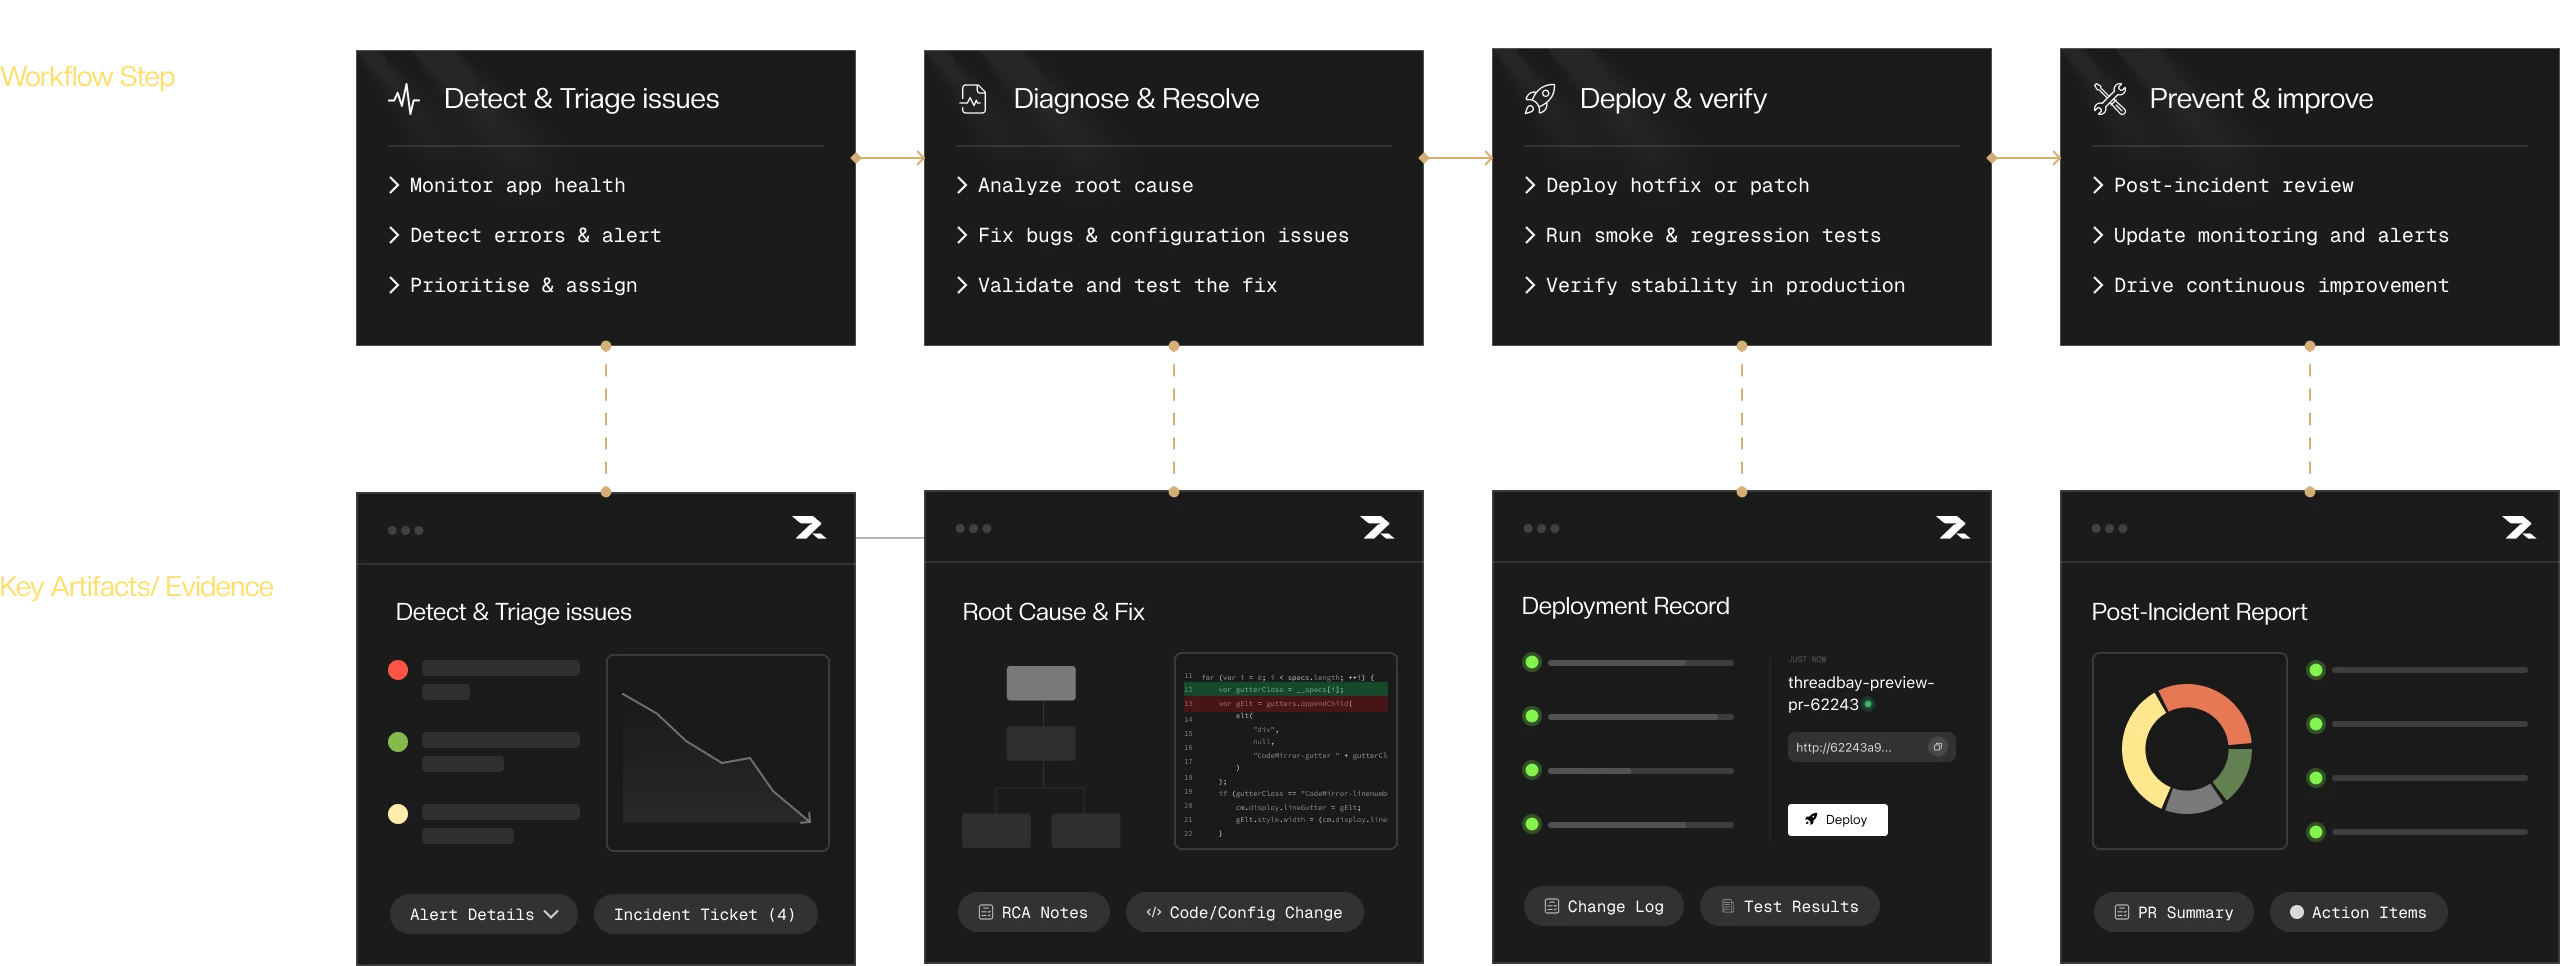
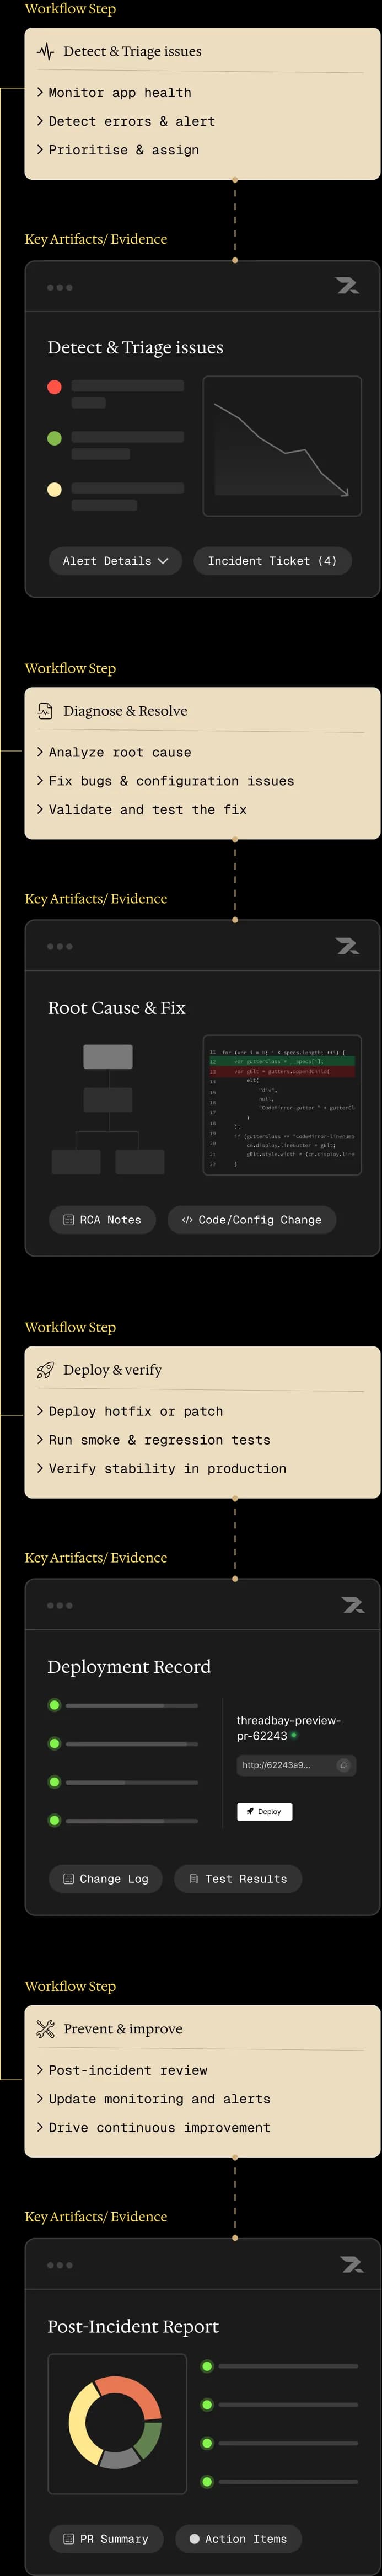
Operate apps
Keep apps healthy, secure, and reliable-every day.
SOLUTION
What Revolte executes for security and performance teams
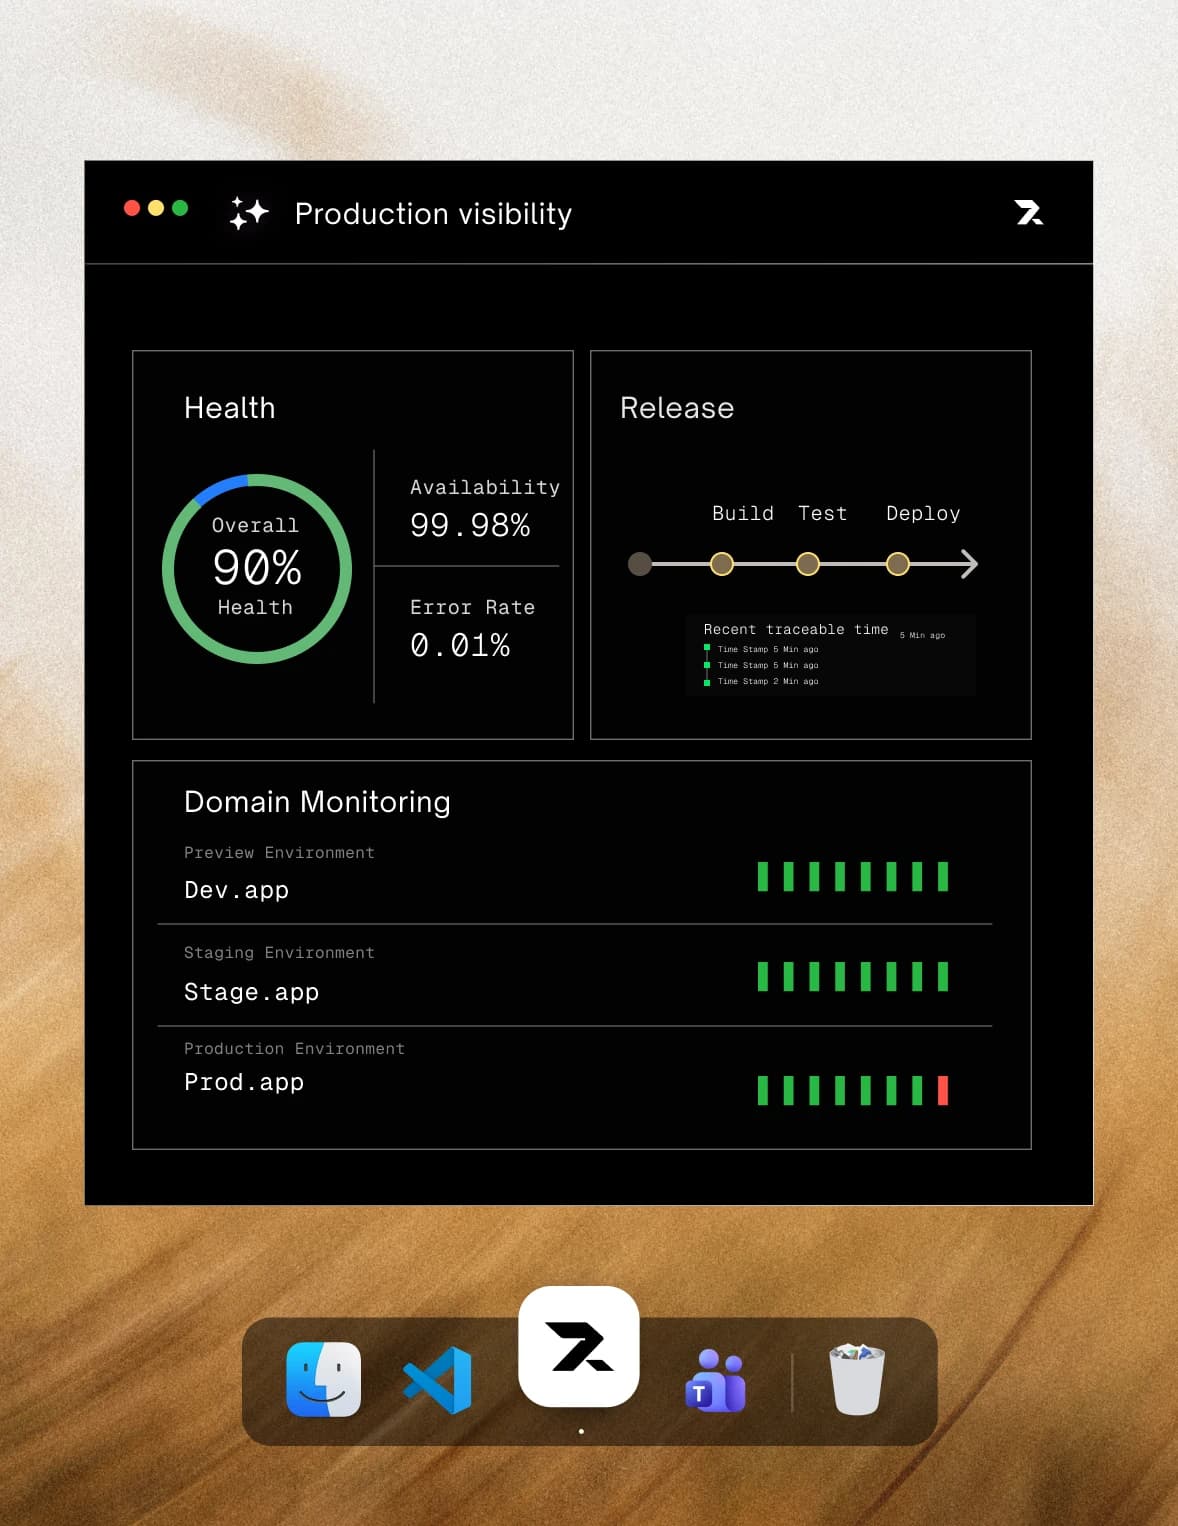
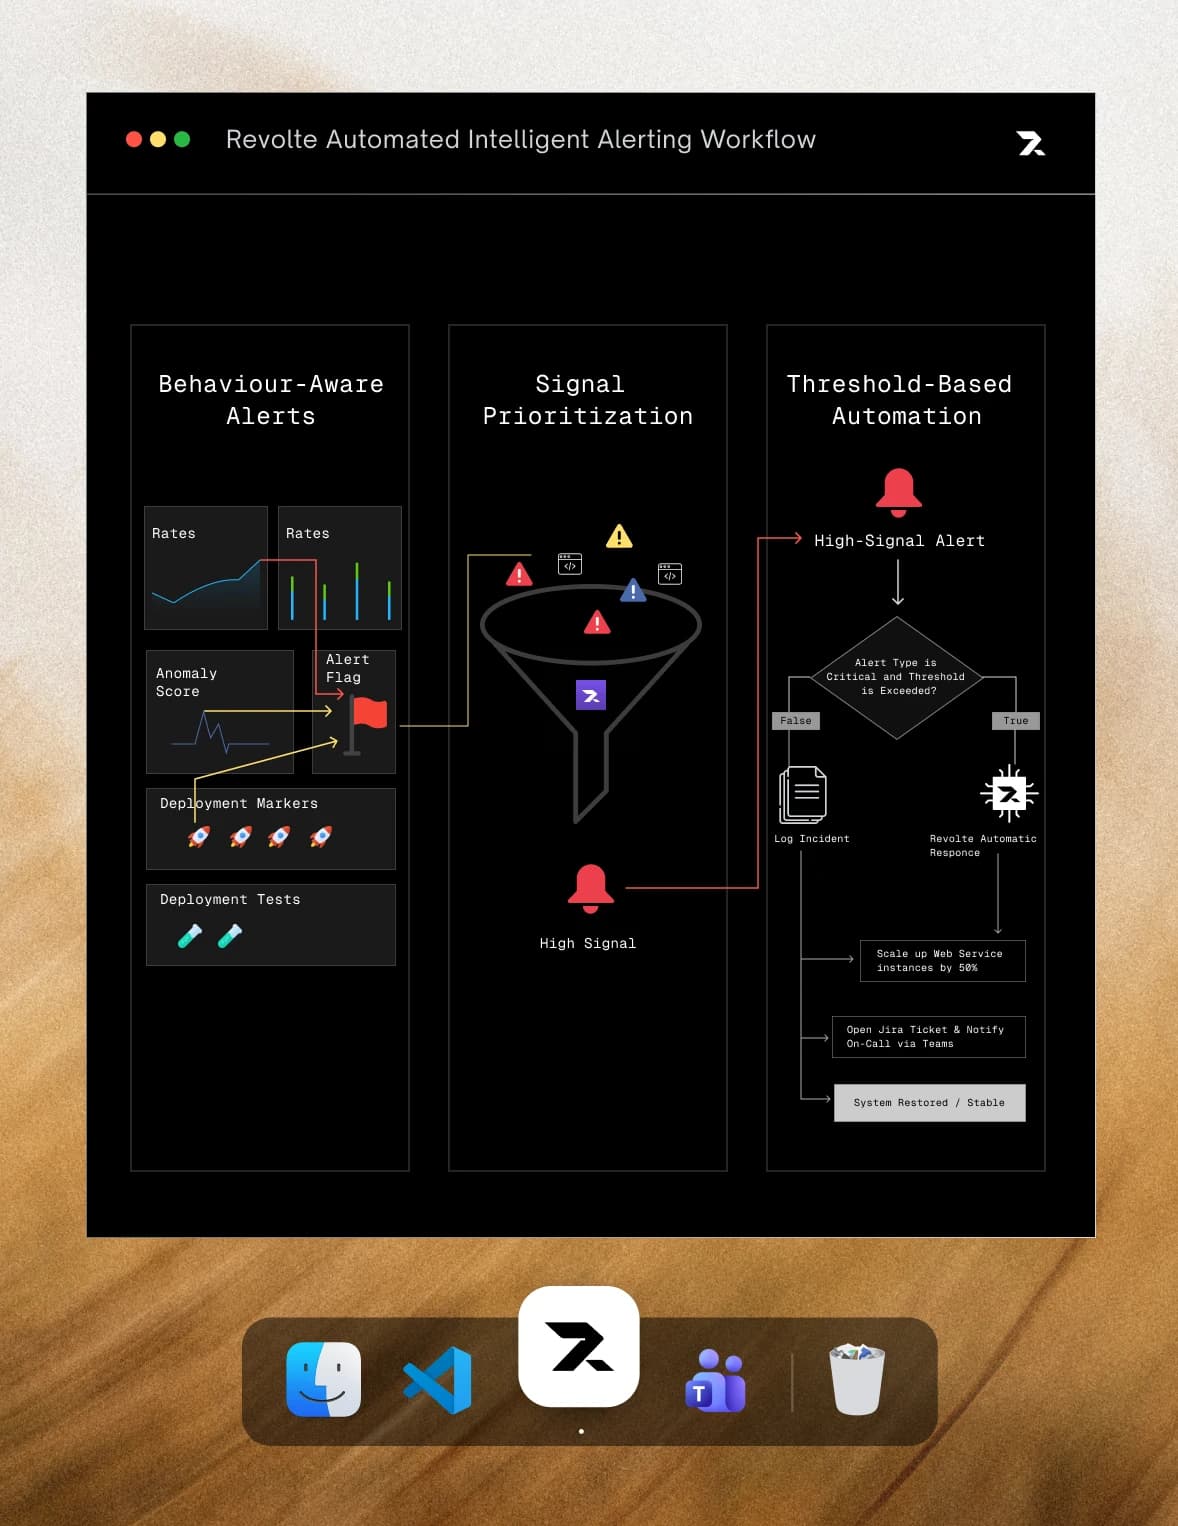
Close findings, don't just file them
Turn scanner output into remediated, validated code.
Reachability analysis
Separates exploitable paths from noise in the dependency graph.
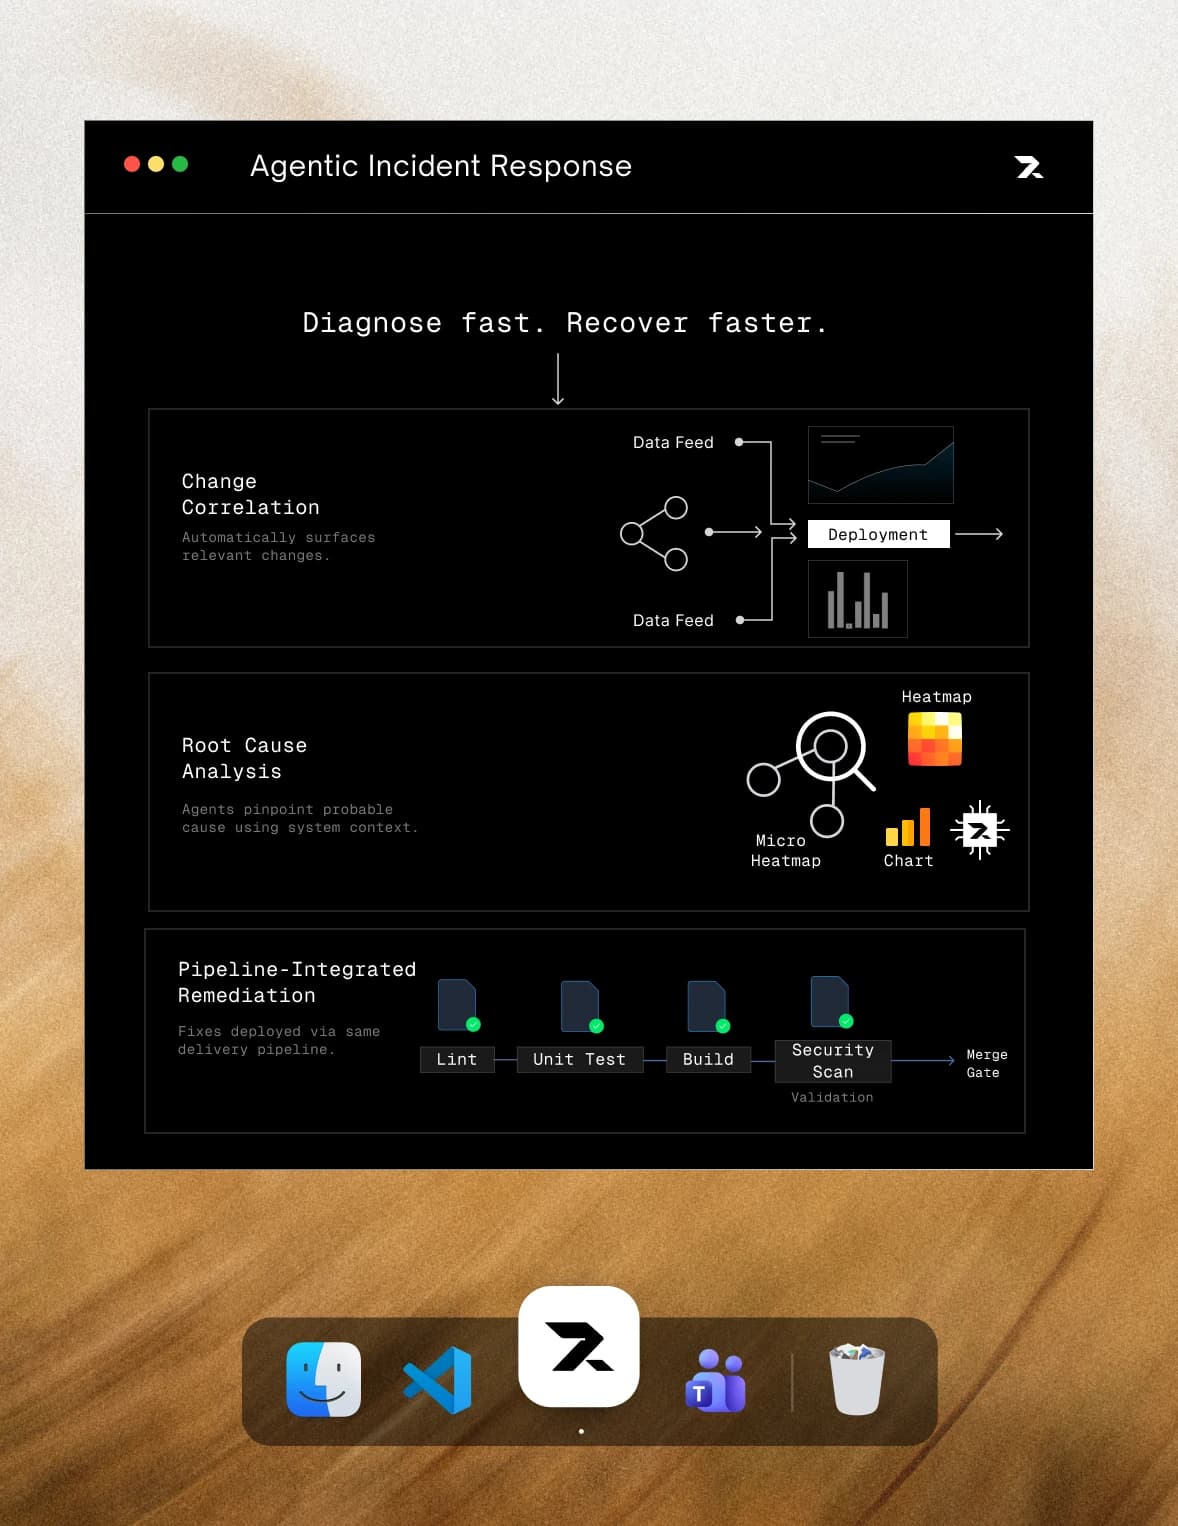
Fix generation
Produces the patch or upgrade and resolves what it breaks.
Closure verification
Re-runs the scan against the fix before the PR is reviewable.

PROOF
Cut critical exposure without freezing the release train
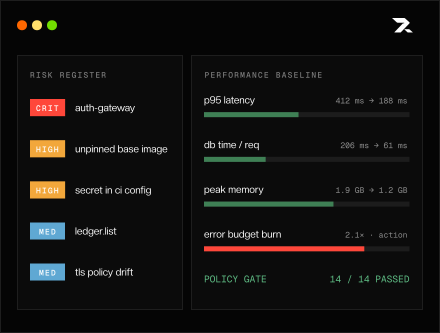
 Critical and high findings appeared on a live payments platform while release frequency stayed steady through governed remediation and policy gates.
CORE VALUE PROPOSITION
A provable way to stay secure and fast
Find what actually matters
Findings are ranked by exploitability, reachability, and blast radius, so remediation effort goes to the risk that is real rather than the risk with the loudest score.
Fix with proof, not just a patch
Every remediation is re-scanned, benchmarked, and regression-checked before it becomes reviewable. A closed finding is demonstrated, not asserted.
Performance is a gate, not a postmortem
Latency and resource cost are measured against a recorded baseline on every change, so degradation is caught before users find it.
Compliance evidence is a byproduct
Policy checks, control mappings, and the trail behind each decision are generated as the work happens instead of assembled before an audit.
Designed for security-critical delivery work
Proof, not just findings
Every remediation carries the scan result, benchmark, and validation that closed it.
Proof, not just findings
Every remediation carries the scan result, benchmark, and validation that closed it.
Security and speed in one pass
Both are validated in the same execution flow instead of competing for the same release window.
Security and speed in one pass
Both are validated in the same execution flow instead of competing for the same release window.
Policy enforced at execution time
Standards run as gates inside the workflow, not as a review stage bolted on at the end.
Policy enforced at execution time
Standards run as gates inside the workflow, not as a review stage bolted on at the end.
Works against your real runtime
Live traffic patterns, actual dependency trees, and production load shape what gets fixed first.
Works against your real runtime
Live traffic patterns, actual dependency trees, and production load shape what gets fixed first.
Harden live systems without slowing the release train
Start BuildingFrequently Asked
Questions
Yes. Revolte is designed to operate in live production environments after software is deployed. Revolte’s AI agents support monitoring, incident detection, remediation workflows, validation, observability, governed releases, and runtime operations across active production systems while engineers maintain operational oversight and approval control.